Rsyslog Template
Rsyslog Template - Easily manage your team's tasks from anywhere in the modern world. You need to open port 514 in the. You must deploy the aws cloudformation template in the aws account where you intend to store your log data. 随 rsyslog 版本不同,如果有如下警告信息,则将 ~ 修改为 stop。. In the next step we need to create a template for remote messages, and tell rsyslog daemon how to record messages received from other client machines. Each log entry have topic which describes the origin of log message. # systemctl restart rsyslog firewall. There can be more than one topic assigned to log message. Amazon cloudwatch logs destinations deploy in the primary account and are created with the required permissions in. Graylog is able to accept and parse rfc 5424 and rfc 3164 compliant syslog messages and supports tcp transport with both the octet counting or termination character methods.

搭建rsyslog日志服务器 Bypass 博客园

如何使用CentOS / RHEL中的Rsyslog创建集中式日志服务器7
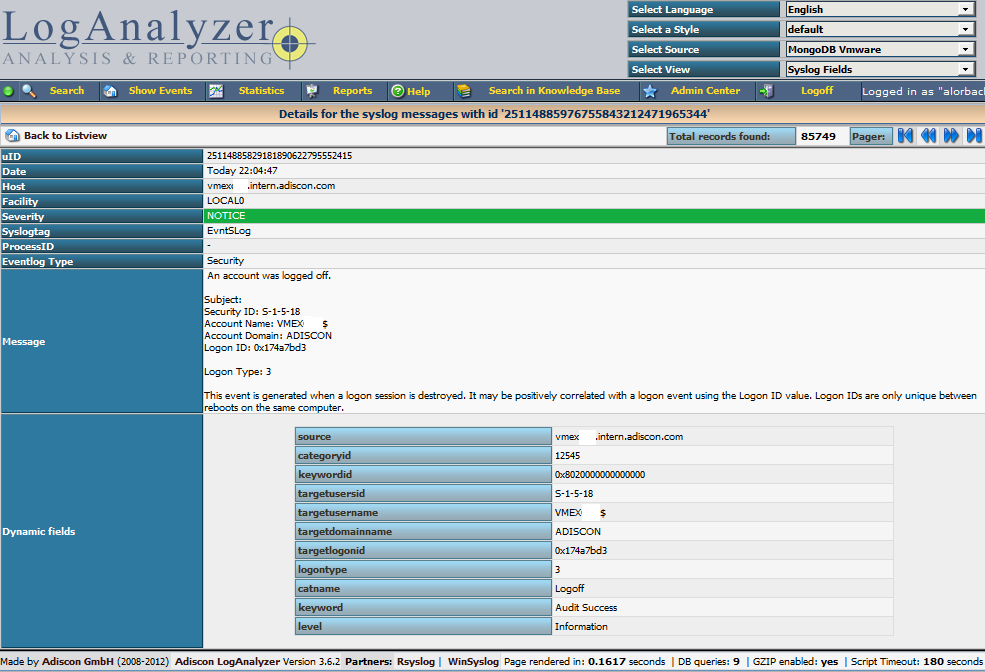
Using MongoDB with rsyslog and LogAnalyzer rsyslog

Configure Rsyslog Centralized Log Server on Ubuntu 20.0418.04

[SOLVED] [6.9.0beta25] through [6.9.0RC1] Syslog Server Broken, Error
使用rsyslog+loganalzey收集日志显示客户端ip图灵社区
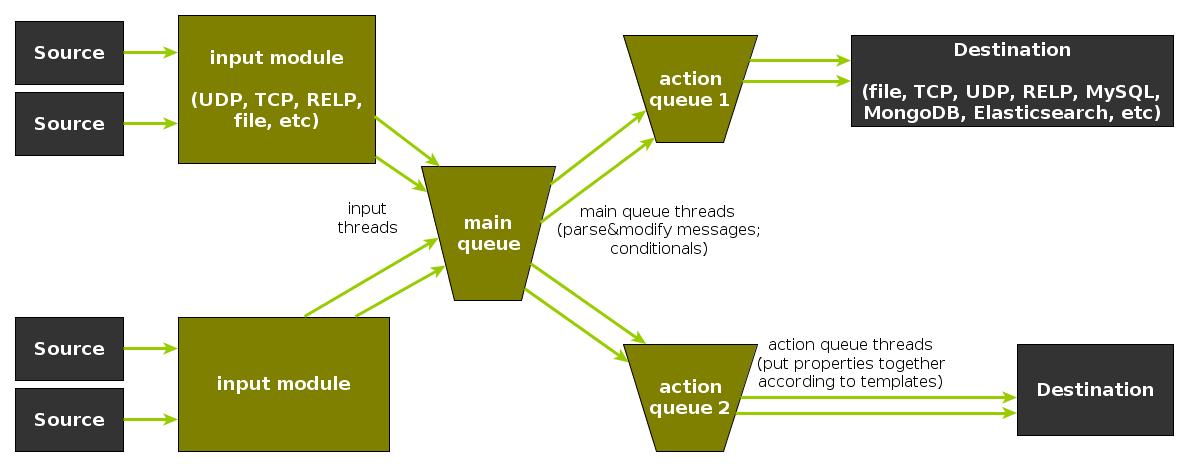
Rsyslog 8.1 Elasticsearch Output Performance Sematext
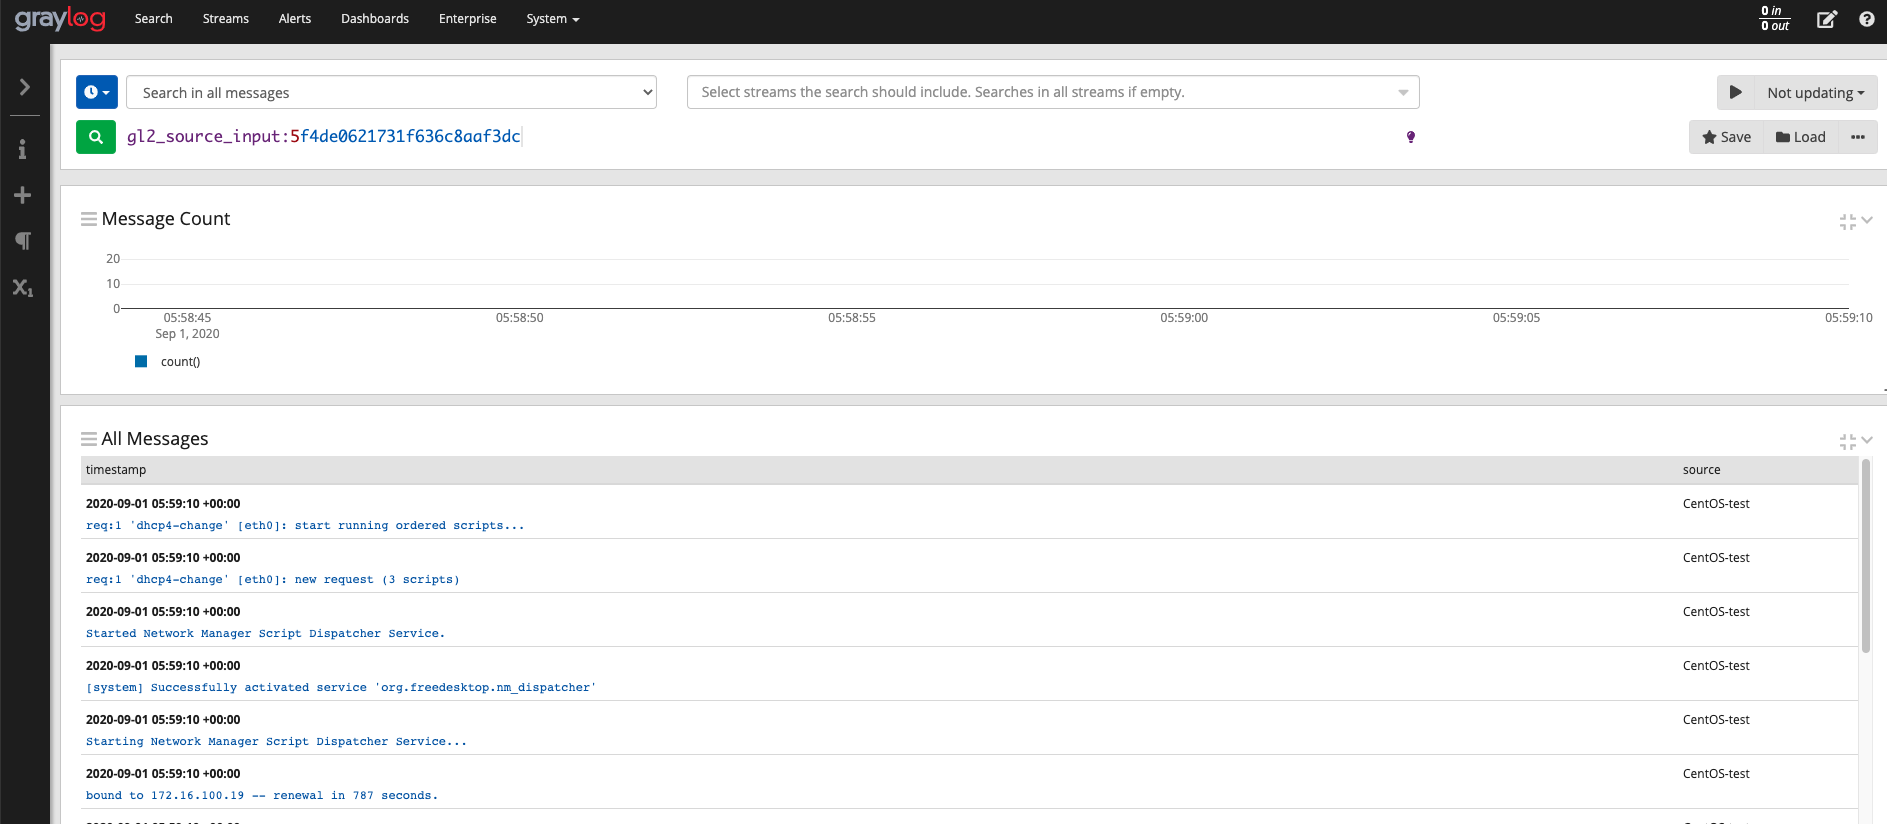
graylog日志系统接收rsyslog日志(二) Allen技术博客
You Must Deploy The Aws Cloudformation Template In The Aws Account Where You Intend To Store Your Log Data.
Udp is also supported and the recommended way to send log messages in most architectures. The centralized logging on aws solution contains the following components: You need to open port 514 in the. Rsyslog uses port 514 for network connectivity, whether it's using tcp or udp.
There Are Many Different Template Options Available Online.
Many devices, especially routers and firewalls, do not send rfc compliant syslog messages. In this step, we will configure our centralized rsyslog server to use a json template to format the log data before sending it to logstash, which will then send it to elasticsearch on a different server. Easily manage your team's tasks from anywhere in the modern world. Each log entry have topic which describes the origin of log message.
In The Next Step We Need To Create A Template For Remote Messages, And Tell Rsyslog Daemon How To Record Messages Received From Other Client Machines.
Once you've uncommented the transport layer protocol and set a template, save your changes to the file. Log ingestion, log indexing, and visualization. Amazon cloudwatch logs destinations deploy in the primary account and are created with the required permissions in. Clickup is the online solution to let your team get more done!
Open /Etc/Rsyslog.conf With A Text Editor, And Append The Following Template Before The Global Directives Block:
Create a template for log receipt. Start with a tailored template for your projects and tasks, and build the workflow and process you need with the tools at your fingertips. For example, ospf debug logs have four different topics: # systemctl restart rsyslog firewall.