Nist 800-171 Access Control Policy Template
Nist 800-171 Access Control Policy Template - February 2020 (includes updates as of january 28, 2021) supersedes: Extensible access control markup language (xacml) and next generation access control (ngac). The fundamental principles (tenets) of information security are confidentiality, integrity, and availability. Together, they are called the cia triad. As components of the template, not the policy. Every element of an information security program (and every security control put in place by an entity) should be designed to achieve one or more of these principles. The exception is the parameters property that passes values from the policy to the template. A comparison of attribute based access control (abac) standards for data service applications: With aws, you control where your data is stored, who can access it, and what resources your organization is consuming at any given moment. Cmvp validation authority updates to iso/iec 24759 and.
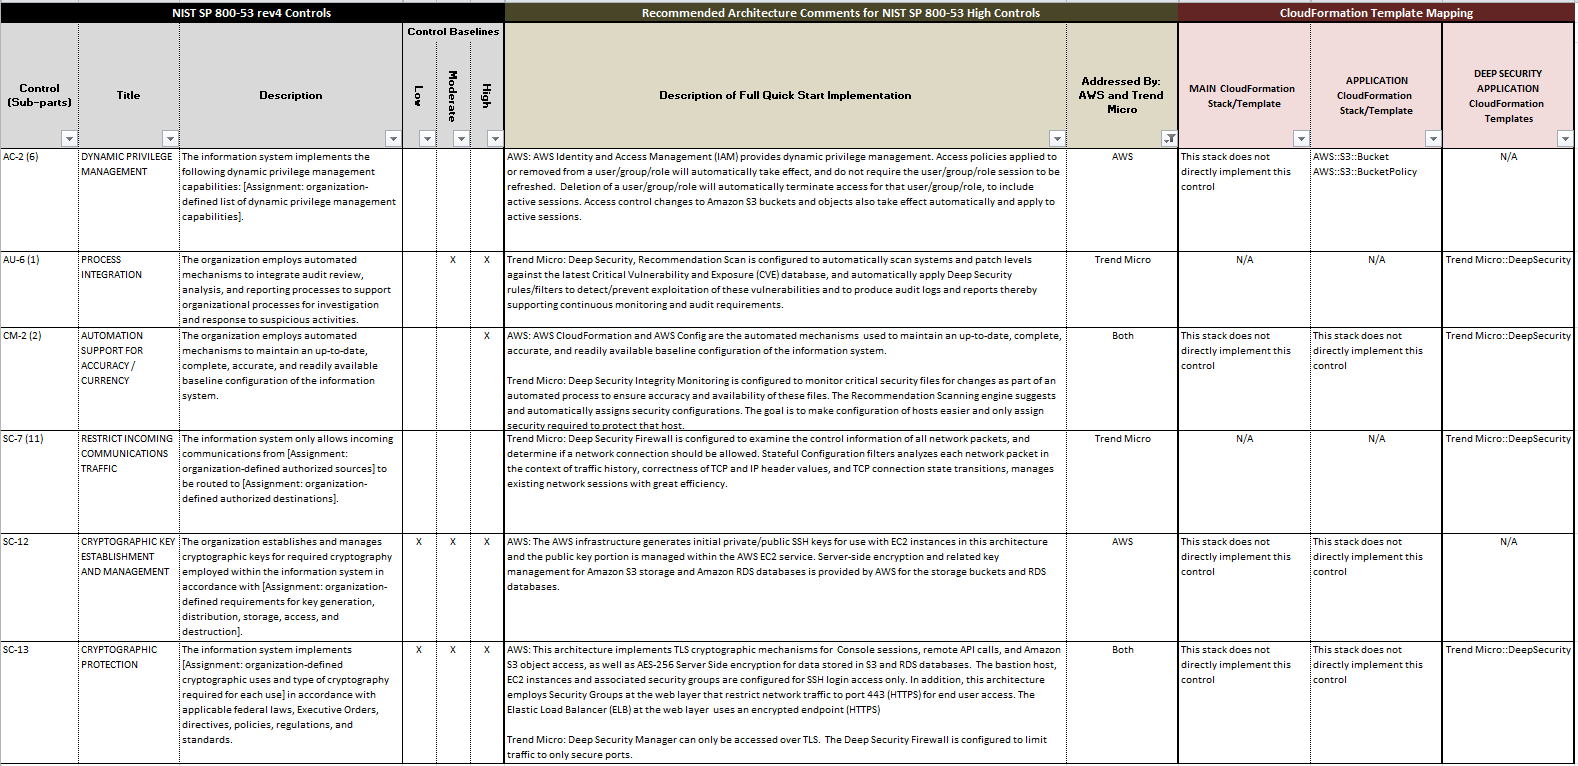
Nist Policy Templates

Nist 800 171 Poa&m Template Template 1 Resume Examples 05KAgna8wP
Nist 800 171 Access Control Policy Template Template 1 Resume
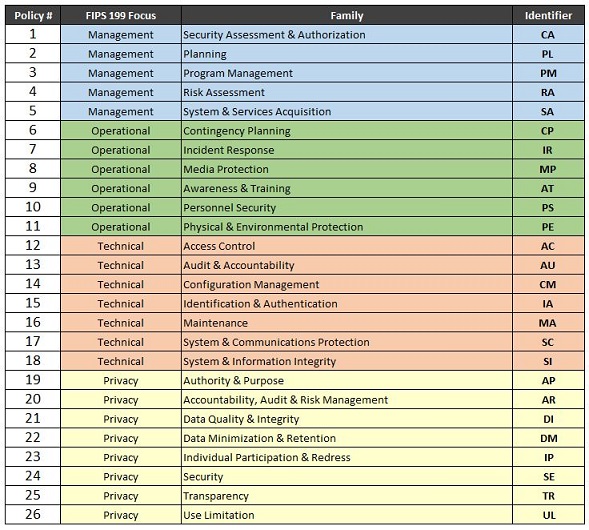
Nist Policy Templates
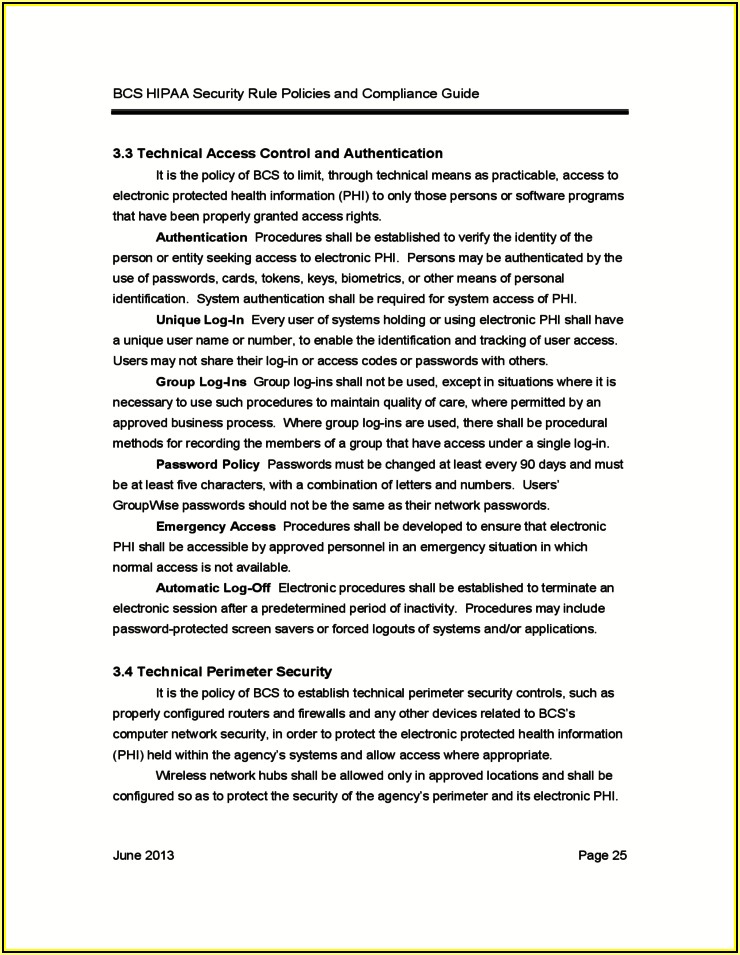
Information Security Policy Template Nist Template 1 Resume

NIST Cyber Security Framework Security Line Card

Nist 800 171 Access Control Policy Template Templates MTAwNjkx
It Security Policy Template Nist Template 1 Resume Examples 7NYAXnb9pv
A Comparison Of Attribute Based Access Control (Abac) Standards For Data Service Applications:
Cmvp validation authority updates to iso/iec 24759 and. The exception is the parameters property that passes values from the policy to the template. With aws, you control where your data is stored, who can access it, and what resources your organization is consuming at any given moment. February 2020 (includes updates as of january 28, 2021) supersedes:
Extensible Access Control Markup Language (Xacml) And Next Generation Access Control (Ngac).
The fundamental principles (tenets) of information security are confidentiality, integrity, and availability. Together, they are called the cia triad. As components of the template, not the policy. Every element of an information security program (and every security control put in place by an entity) should be designed to achieve one or more of these principles.